
CAS-005 Sample Questions & Answers
Automation, scripting and advanced cryptography carry the heaviest weight, alongside cloud security capabilities and data-control strategies, program documentation and governance frameworks, and threat hunting with monitoring and data analysis.
Launch the full CAS-005 simulator →Showing 10 of 20 free samples.
- Question 1IntermediateSelect 2
Company A is merging with Company B. Company A is a small, local company. Company B has a large, global presence. The two companies have a lot of duplication in their IT systems, processes, and procedures. On the new Chief Information Officer's (CIO's) first day, a fire breaks out at Company B's main data center. Which of the following actions should the CIO take first?
Show answer & explanation
Correct answers: A, C
- Question 2IntermediateSelect 2
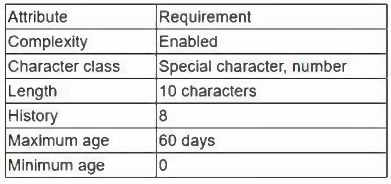
The results of an internal audit indicate several employees reused passwords that were previously included in a published list of compromised passwords.The company has the following employee password policy:Which of the following should be implemented to best address the password reuse issue? (Choose two.)
Show answer & explanation
Correct answers: A, B
- Question 3Intermediate
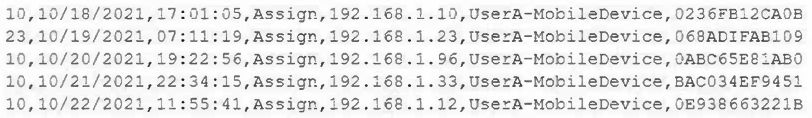
A mobile administrator is reviewing the following mobile device DHCP logs to ensure the proper mobile settings are applied to managed devices:Which of the following mobile configuration settings is the mobile administrator verifying? A.Service set identifier authenticationB.Wireless network auto joiningC.802.1X with mutual authenticationD.Association MAC address randomization
Show answer & explanation
Correct answer: D
- Question 4Intermediate
A security analyst is investigating a possible insider threat incident that involves the use of an unauthorized USB from a shared account to exfiltrate data. The event did not create an alert. The analyst has confirmed the USB hardware ID is not on the device allow list, but has not yet confirmed the owner of the USB device. Which of the following actions should the analyst take next?
Show answer & explanation
Correct answer: B
- Question 5Intermediate
Which of the following security features do email signatures provide?
Show answer & explanation
Correct answer: A
- Question 6Advanced
Security Architecture · Implement identity and access management in a cloud/hybrid environment
A financial services firm is architecting a new cloud-native trading platform using microservices deployed on Kubernetes. To comply with Zero Trust principles, the Chief Architect mandates that service-to-service communication must be authenticated using short-lived, cryptographically verifiable identities, without relying on static secrets like API keys stored in environment variables. The solution must automatically issue and rotate these identities for all workloads. Which of the following technologies should be implemented to meet these requirements?
Show answer & explanation
Correct answer: C
SPIFFE (Secure Production Identity Framework for Everyone) and its reference implementation, SPIRE (SPIFFE Runtime Environment), are designed specifically for this use case. They provide a standardized way to issue, validate, and rotate short-lived cryptographic identities (called SVIDs - SPIFFE Verifiable Identity Documents) to workloads automatically. This eliminates the need for static secrets and provides a strong foundation for Zero Trust service-to-service authentication in dynamic environments like Kubernetes.
- Question 7IntermediateSelect 3
Security Engineering · Given a scenario, use security automation and orchestration to improve efficiency
A security engineer is tasked with creating a SOAR playbook to automate the initial response to a suspected phishing email reported by an employee. The goal is to enrich the indicators of compromise (IOCs) from the email and take initial containment actions without human intervention. Which THREE of the following actions should be included in the automated playbook? (Select THREE)
Show answer & explanation
Correct answers: A, B, D
A standard SOAR playbook for phishing involves automated enrichment and containment. Submitting IOCs to a sandbox and querying threat intelligence are key enrichment steps. Adding confirmed malicious IOCs to preventative tools like EDR and web proxies is a crucial automated containment step. Deleting all emails from a sender is too aggressive for an automated initial action, as it could be a spoofed legitimate sender, impacting business operations.
- Question 8Intermediate
Governance, Risk, and Compliance · Summarize risk management processes and concepts
A global logistics company is conducting a risk assessment of its supply chain software. The assessment reveals that a critical third-party shipping API, which is integrated into their primary logistics platform, has no SLA for security patching and uses a static, long-lived API key for authentication. The vendor has stated they have no immediate plans to upgrade their API security. The company cannot replace this vendor for at least 18 months due to contractual obligations. Which risk treatment strategy is most appropriate for the company to adopt in the short term?
Show answer & explanation
Correct answer: C
Risk Mitigation involves taking active steps to reduce the likelihood or impact of a risk. Since the company cannot avoid the risk (by stopping use of the API) or transfer it contractually in the short term, the best approach is to implement compensating controls. This could include wrapping the API calls in a secure facade, implementing strict monitoring and alerting on its usage, and restricting the IP addresses that can call the API, thereby mitigating the associated risks.
- Question 9Advanced
Security Engineering · Implement endpoint security controls
A security architect is designing a defense-in-depth strategy for a large enterprise. The Chief Information Security Officer (CISO) is concerned about the increasing threat of attackers using legitimate administrative tools like PowerShell for lateral movement, a technique often referred to as 'living off the land'. The CISO wants a solution that restricts PowerShell usage to only signed, approved scripts and specific interactive commands required for administrative duties, while logging all other activity. Which of the following technologies would be MOST effective in achieving this?
Show answer & explanation
Correct answer: B
PowerShell Just Enough Administration (JEA) is a security technology designed specifically for this purpose. It allows for role-based administration through PowerShell, enabling administrators to create constrained endpoints that expose only a specific, approved set of cmdlets, functions, and external commands to users. This directly addresses the requirement to limit interactive commands and can be configured to enforce script signing, effectively preventing the execution of unauthorized PowerShell code and mitigating 'living off the land' attacks.
- Question 10Beginner
Security Operations · Explain the use of threat intelligence in security operations
A threat intelligence analyst is reviewing indicators from a recent campaign targeting financial institutions. The indicators are provided in STIX 2.1 format. The analyst needs to extract the specific command-and-control (C2) domains that the malware communicates with. Which STIX Domain Object (SDO) would contain this information?
Show answer & explanation
Correct answer: C
In the STIX (Structured Threat Information eXpression) data model, the 'Indicator' SDO is used to represent specific, actionable intelligence like malicious domains, IP addresses, or file hashes. The 'pattern' property of the Indicator object would contain an expression, such as
[domain-name:value = 'evil-c2.com'], which directly identifies the C2 domain.
Ready for the real thing?
The full CAS-005 simulator has every exam-style question, timed mode, and instant scoring.